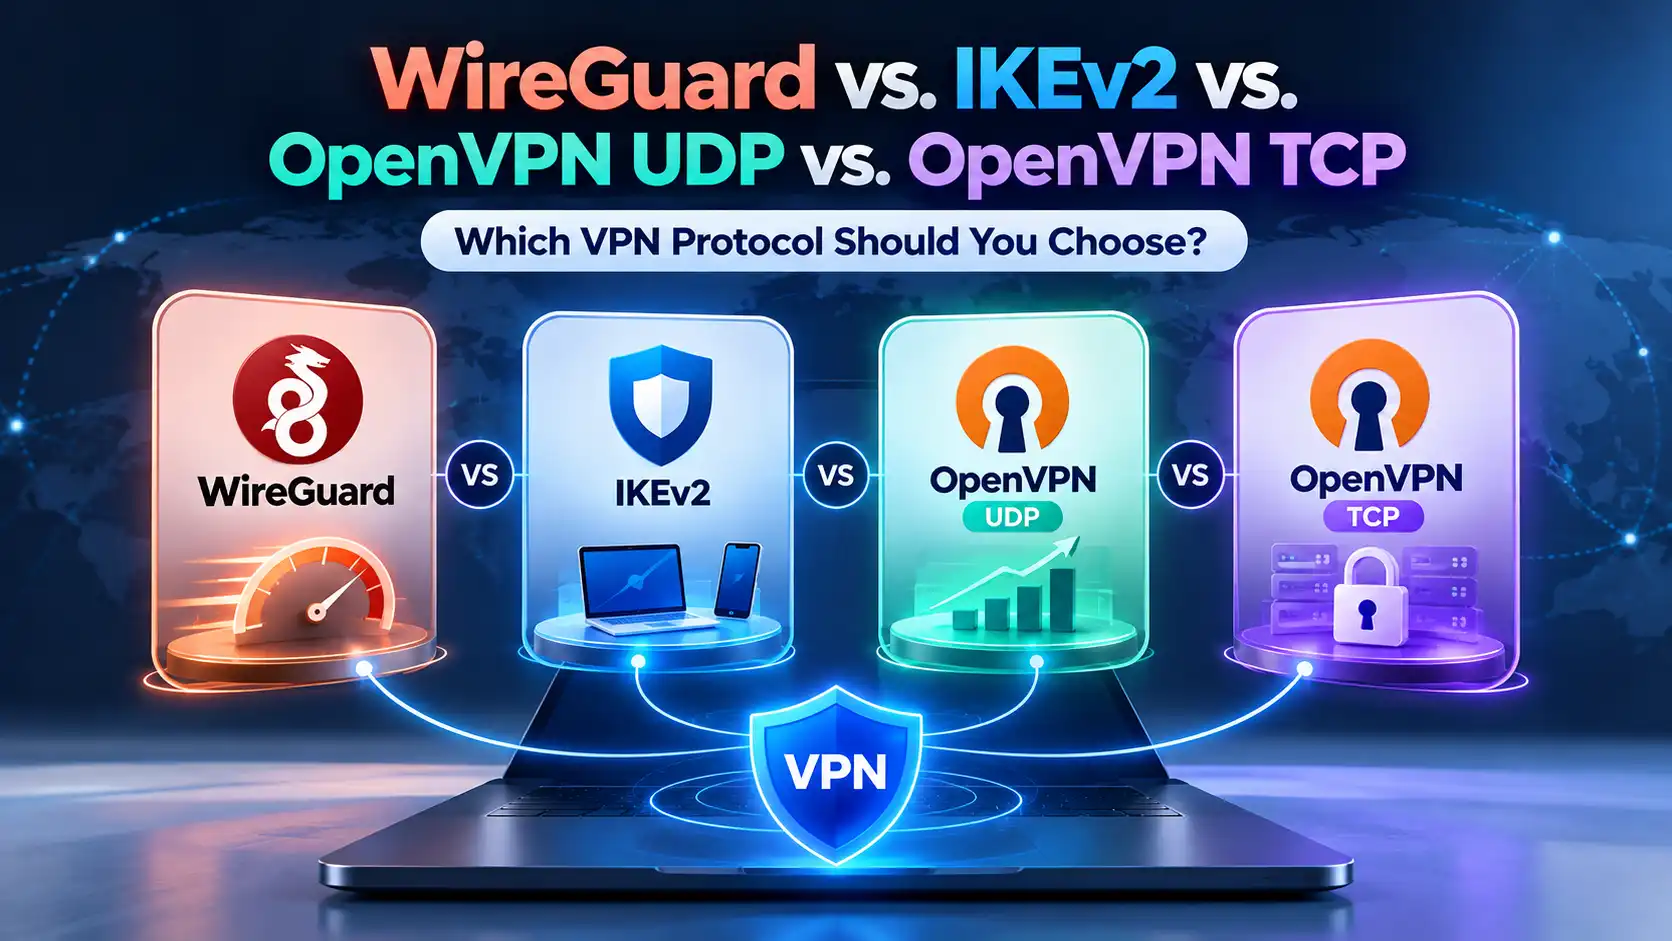
Choosing a VPN protocol can make a noticeable difference in how your connection performs. Some protocols prioritize speed and efficiency, while others offer greater flexibility on restrictive networks or handle network changes particularly well.
Four common options are WireGuard, IKEv2/IPsec, OpenVPN UDP, and OpenVPN TCP. All can provide secure VPN connections when properly implemented, but they work differently and are suited to different situations.
Quick answer: WireGuard is an excellent starting point for fast, everyday VPN use. IKEv2/IPsec is particularly useful for mobile connections that frequently switch networks. OpenVPN UDP offers a balance of security, compatibility, and performance. OpenVPN TCP is worth trying when UDP connections are restricted or fail.
The best choice depends on your network, device, and what you want from your VPN.
What Is a VPN Protocol?
A VPN protocol is a set of rules that determines how your device establishes and maintains a secure connection with a VPN server.
It helps manage authentication, encryption, and the transmission of data between your device and the server.
Different protocols use different technologies to achieve these goals. That is why switching protocols can sometimes improve connection speed, compatibility, or reliability.
One important distinction: OpenVPN UDP and OpenVPN TCP are not two completely separate VPN protocols. They are two transport modes of OpenVPN, using UDP and TCP respectively.
VPN Protocol Comparison at a Glance
Feature | WireGuard | IKEv2/IPsec | OpenVPN UDP | OpenVPN TCP |
|---|---|---|---|---|
Typical speed | Very fast | Fast | Fast to moderate | Often slower |
Security | Strong modern cryptography | Strong when properly configured | Strong when properly configured | Strong when properly configured |
Connection efficiency | Excellent | Good | Good | Lower in many conditions |
Mobile network switching | Generally good | Excellent with MOBIKE support | Depends on implementation | Depends on implementation |
Restrictive networks | May be blocked | May be blocked | May be blocked | Can help when UDP is blocked |
Main advantage | Speed and efficiency | Mobility | Balanced performance | TCP compatibility |
Best starting use | Everyday browsing, gaming, streaming | Mobile connections | General-purpose alternative | Networks restricting UDP |
These are general characteristics, not guaranteed performance rankings. Actual results depend on the VPN implementation, server, device, and network.
1. WireGuard: Built for Speed and Efficiency
WireGuard is a modern, open-source VPN protocol designed to be lightweight, secure, and efficient.
Unlike older protocols with many configurable components, WireGuard uses a comparatively streamlined design and a defined set of modern cryptographic algorithms.
Its efficient architecture can help deliver fast connections with relatively low processing overhead.
Key Advantages of WireGuard
High performance: Often delivers excellent speeds and low latency.
Efficient design: Its lightweight implementation can reduce processing overhead.
Modern security: Uses established cryptographic components, including ChaCha20 and Poly1305.
Fast connection establishment: Designed to establish secure connections efficiently.
Good everyday usability: Well suited to browsing, video calls, streaming, and gaming.
Potential Limitations
WireGuard normally uses UDP transport. Networks that restrict UDP or identify and block WireGuard traffic may interfere with the connection.
WireGuard also does not include built-in traffic obfuscation. Some VPN providers offer additional technologies to address this, but those features are separate from the standard WireGuard protocol.
When Should You Choose WireGuard?
WireGuard is a strong first choice when you want:
Fast everyday browsing
Smooth streaming
Responsive online gaming
Efficient VPN performance
A modern protocol with strong security
Best for: Users who prioritize speed, efficiency, and everyday performance.
2. IKEv2/IPsec: Designed for Mobility
IKEv2 stands for Internet Key Exchange version 2. It is commonly used together with IPsec, which provides the protection for VPN traffic.
One of its notable strengths is its ability to handle changes in network connectivity.
With support for an extension called MOBIKE, an IKEv2/IPsec connection can adapt when a device changes IP addresses or moves between networks.
For example, imagine leaving home while using your phone. Your connection changes from Wi-Fi to mobile data. An IKEv2/IPsec implementation with MOBIKE support can update the connection without necessarily establishing a completely new VPN session.
Key Advantages of IKEv2/IPsec
Strong security: Supports modern cryptographic configurations.
Fast performance: Can provide efficient VPN connections.
Mobile-friendly design: MOBIKE supports changes in network addresses.
Good operating-system integration: Supported by many major platforms.
Stable mobility: Useful for devices that frequently change networks.
Potential Limitations
IKEv2/IPsec commonly uses UDP ports 500 and 4500, which may be restricted by some networks.
Its security and performance also depend on the chosen cryptographic configuration and implementation.
Although IKEv2/IPsec can be an excellent mobile option, it is not automatically faster or more reliable than every alternative.
When Should You Choose IKEv2/IPsec?
IKEv2/IPsec is worth considering when:
You frequently move between Wi-Fi and mobile data.
You use a VPN on a phone or tablet.
Your device and VPN provider support it.
You want a secure connection with strong mobility support.
Best for: Mobile users whose networks change frequently.
3. OpenVPN UDP: A Balance of Security and Performance
OpenVPN is an established, open-source VPN protocol with a long history of real-world deployment.
It can use either UDP or TCP to transport VPN traffic.
UDP, or User Datagram Protocol, sends packets without requiring the transport layer to acknowledge and retransmit every packet.
This reduces transport overhead and makes UDP a practical choice for VPN connections where performance matters.
OpenVPN is designed to operate efficiently over UDP.
Key Advantages of OpenVPN UDP
Mature technology: OpenVPN has been widely deployed and examined.
Strong security: Supports secure encryption and authentication configurations.
Good performance: UDP avoids some of the overhead associated with TCP.
Broad compatibility: Supported across many devices and operating systems.
Flexible configuration: Can work in a wide range of network environments.
Potential Limitations
OpenVPN UDP may be slower than WireGuard in some environments.
Networks that block or restrict UDP traffic may also prevent it from connecting.
UDP itself does not guarantee delivery of every packet, but that does not mean applications using an OpenVPN UDP tunnel automatically lose reliable communication. Applications such as web browsers can still use TCP or other reliability mechanisms inside the tunnel.
When Should You Choose OpenVPN UDP?
Try OpenVPN UDP when:
You want a well-established VPN protocol.
WireGuard is unavailable or performs poorly on your network.
You need broad compatibility.
You want a practical balance between performance and security.
Best for: Users seeking a mature, versatile alternative to WireGuard.
4. OpenVPN TCP: Useful on Restrictive Networks
OpenVPN TCP uses Transmission Control Protocol to carry VPN traffic.
Unlike UDP, TCP includes mechanisms for ordered delivery, acknowledgments, and retransmission of lost data.
These mechanisms are valuable in many internet applications. However, using TCP as the transport for an entire VPN tunnel can introduce additional overhead.
For example, when a TCP application runs inside a TCP-based VPN tunnel, the two layers may respond to packet loss in ways that reduce performance.
This is sometimes called the TCP-over-TCP problem.
So why use OpenVPN TCP?
Because some networks restrict UDP traffic while allowing TCP connections.
When a VPN provider supports an appropriate TCP configuration, OpenVPN TCP may connect successfully where UDP-based options fail.
Key Advantages of OpenVPN TCP
Compatibility with certain restrictive networks: Can be useful where UDP traffic is blocked.
Reliable transport mechanisms: TCP handles packet ordering and retransmission.
Flexible configuration: OpenVPN can operate over different TCP ports.
Established security: Uses the same underlying OpenVPN security architecture when properly configured.
Potential Limitations
OpenVPN TCP can experience:
Lower speeds
Higher latency
Additional retransmission overhead
Performance problems on congested or lossy networks
It is also important to understand that TCP does not automatically make a VPN connection more stable.
Its main practical advantage is often network compatibility rather than better overall performance.
OpenVPN TCP can sometimes use port 443, which is commonly associated with HTTPS. However, this does not make VPN traffic invisible or guarantee that it can bypass advanced network restrictions.
When Should You Choose OpenVPN TCP?
Try OpenVPN TCP when:
WireGuard fails to connect.
OpenVPN UDP is blocked or unreliable.
Your network restricts UDP traffic.
Connection compatibility matters more than maximum speed.
Best for: Networks where UDP-based VPN connections cannot establish or maintain a usable connection.
OpenVPN UDP vs. TCP: What Is the Real Difference?
The biggest difference is how data is transported.
UDP is designed for low-overhead packet delivery. TCP adds transport-level mechanisms to manage ordering, acknowledgments, and retransmissions.
For VPN traffic, these differences affect performance and network compatibility.
Comparison | OpenVPN UDP | OpenVPN TCP |
|---|---|---|
Transport behavior | Connectionless | Connection-oriented |
Packet retransmission at transport layer | No | Yes |
Typical VPN performance | Usually better | Often slower |
Latency overhead | Generally lower | Can be higher |
Compatibility with UDP-restricted networks | Limited | Often better |
Preferred use | Everyday VPN connections | Troubleshooting restrictive networks |
The key takeaway: UDP is generally the preferred OpenVPN transport when it works properly. TCP is a useful alternative when network restrictions make UDP impractical.
Which VPN Protocol Is the Fastest?
For many users, WireGuard is an excellent starting point for speed.
Its lightweight design and modern cryptography help it perform efficiently across a wide range of devices.
IKEv2/IPsec can also deliver strong performance, while OpenVPN UDP generally offers a good balance between speed and compatibility.
OpenVPN TCP often has more overhead, particularly when carrying TCP-based applications over unstable networks.
However, there is no universal speed ranking that applies to every device or network.
Server distance, congestion, hardware, encryption implementation, routing, and local network conditions can all influence the result.
The most reliable way to find the fastest option is to compare performance under similar conditions.
Which VPN Protocol Is the Most Secure?
WireGuard, IKEv2/IPsec, and OpenVPN can all provide strong security when implemented and configured correctly.
Their approaches differ:
WireGuard uses a streamlined design and a defined set of modern cryptographic algorithms.
IKEv2/IPsec combines secure connection negotiation with IPsec protection. Its security depends partly on the selected algorithms and configuration.
OpenVPN uses established TLS-based mechanisms and supports a range of secure cryptographic configurations.
Importantly, OpenVPN UDP and OpenVPN TCP are not inherently different security levels. Changing the transport from UDP to TCP does not automatically make the encryption stronger.
A trustworthy VPN provider, secure implementation, proper configuration, and up-to-date software matter just as much as the protocol name.
How to Choose the Right VPN Protocol for Your Situation
Rather than looking for a single winner, match the protocol to the problem you are trying to solve.
Your priority | Recommended starting point |
|---|---|
Fast everyday VPN use | WireGuard |
Gaming and low latency | WireGuard |
Streaming and video calls | WireGuard or OpenVPN UDP |
A mature, widely supported option | OpenVPN UDP |
Frequent Wi-Fi/mobile-data switching | IKEv2/IPsec, when supported |
UDP connections are blocked | OpenVPN TCP |
Unsure which protocol to use in SyncVPN | Smart |
These are starting recommendations, not guarantees. If one option performs poorly, testing another protocol may produce better results.
Choosing a Protocol in SyncVPN
The SyncVPN protocol menu includes a Smart option designed to automatically select a protocol for your connection.
The shown manual options are:
WireGuard
OpenVPN (UDP)
OpenVPN (TCP)
For most users, starting with Smart is the simplest approach.
If you prefer to select a protocol manually, WireGuard is a sensible first choice for everyday performance. OpenVPN UDP is a useful alternative, while OpenVPN TCP is worth testing if UDP-based connections are having trouble.
IKEv2/IPsec is included in this guide as a widely used VPN technology for comparison. It is not shown as a selectable option in the SyncVPN protocol menu described here.
Frequently Asked Questions
Is WireGuard better than OpenVPN?
WireGuard often offers faster performance and lower processing overhead. OpenVPN remains a secure, mature, and flexible alternative. The better choice depends on your device, network, and compatibility requirements.
Is IKEv2 faster than WireGuard?
Both can perform well, but WireGuard is often particularly efficient. Actual speeds depend on implementation, device hardware, server conditions, and network routing. IKEv2/IPsec has an additional advantage when its MOBIKE extension is used for network mobility.
Is OpenVPN TCP more secure than UDP?
Not inherently. Both modes can use the same OpenVPN security mechanisms. TCP changes how traffic is transported, not automatically how strongly it is encrypted.
Why is OpenVPN UDP usually faster than TCP?
UDP has less transport-level overhead. TCP introduces acknowledgment, ordering, retransmission, and congestion-control mechanisms that can add delays when used to carry VPN traffic.
Which protocol is best for gaming?
WireGuard is often a good first choice because of its efficient design and potential for low latency. OpenVPN UDP can also perform well. The server location and quality of your underlying connection remain important.
Which protocol should I try if my VPN will not connect?
Start with your VPN application's automatic selection mode if available. If a UDP-based protocol fails, try OpenVPN TCP. Also consider changing servers and checking your network connection, since the protocol may not be the only cause.
Final Verdict: There Is No Single Best VPN Protocol for Everyone
WireGuard, IKEv2/IPsec, OpenVPN UDP, and OpenVPN TCP each have strengths.
WireGuard stands out for modern design, efficiency, and everyday performance.
IKEv2/IPsec is particularly useful for mobility when the appropriate features are supported.
OpenVPN UDP remains a strong general-purpose option with broad compatibility.
OpenVPN TCP is valuable when network restrictions interfere with UDP connections.
For SyncVPN users, Smart is the easiest starting point. If you want manual control, begin with WireGuard and consider the OpenVPN options when your connection needs a different approach.
The best protocol is ultimately the one that provides a secure, stable, and usable connection on your particular network.