When you connect to a VPN, your internet traffic typically travels through an encrypted tunnel to a VPN server. This helps protect your connection and allows websites to see the VPN server's public IP address instead of your regular public IP address.
But what if you want some applications to use your VPN while others connect directly to the internet?
That's where VPN Split Tunneling comes in.
Split Tunneling is a VPN feature that lets you control which applications or connections use the VPN tunnel and which use your regular internet connection.
Instead of routing everything through the VPN, you can customize how different parts of your internet traffic are handled.
With SyncVPN, the Split Tunneling feature is designed to let users manage which applications and IP addresses are protected by the VPN.
In this guide, we'll explain how Split Tunneling works, when it can be useful, what to consider before enabling it, and how to manage your connection more effectively.
What Is VPN Split Tunneling?
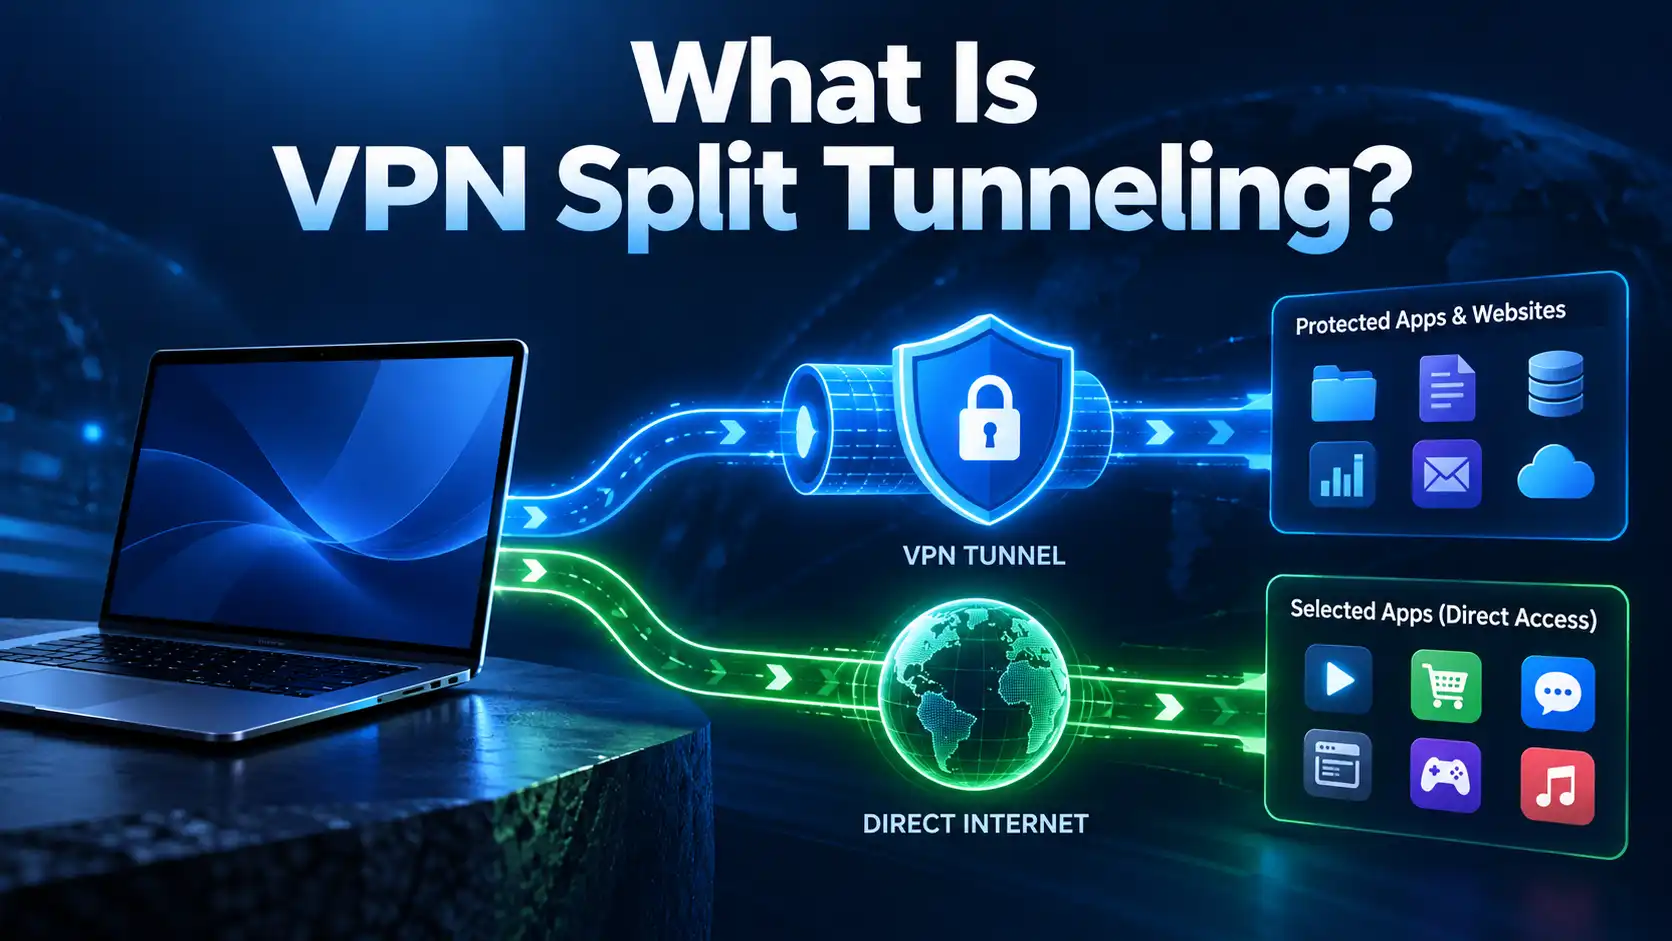
VPN Split Tunneling is a feature that divides your internet traffic into two separate routes:
VPN-protected traffic: Connections that travel through the encrypted VPN tunnel.
Direct internet traffic: Connections that bypass the VPN and use your regular network.
This gives you more flexibility over how your device communicates with websites, applications, and online services.
For example, you might want your web browser to use the VPN while a local application connects directly to the internet.
With a traditional full-tunnel VPN connection, both applications would normally use the VPN.
With Split Tunneling, you can configure different routing rules for different activities.
The result is a more customizable connection that can balance privacy, compatibility, and everyday usability.
How Does Split Tunneling Work?
When a VPN is connected without Split Tunneling, supported internet traffic is generally routed through the VPN server.
Split Tunneling changes this behavior by applying rules that determine which traffic enters the VPN tunnel.
These rules may be based on applications, destination IP addresses, or other supported connection criteria.
Here's a simplified example:
Without Split Tunneling:
You connect your device to a VPN server.
Your browser sends traffic through the VPN.
Your other applications also use the VPN connection.
Websites and services generally see the VPN server's public IP address.
With Split Tunneling:
You connect to the VPN.
You configure which applications or IP addresses should use the VPN.
Selected traffic follows the VPN route.
Traffic configured to bypass the VPN uses your regular internet connection.
Both connection types can operate while the VPN remains connected.
The important difference is that you decide how traffic is routed rather than applying one connection route to everything.
Types of VPN Split Tunneling
Split Tunneling can be implemented in different ways depending on the VPN application and operating system.
Two important distinctions are how traffic is selected and whether the rules include or exclude traffic from the VPN.
Application-Based Split Tunneling
Application-based Split Tunneling allows routing decisions to be made for specific applications.
For example, you might configure:
A web browser to connect through the VPN.
A local application to bypass the VPN.
A work application to remain protected by the VPN.
Another application to use your normal network connection.
This approach is useful when you want different applications to follow different routing rules.
IP Address-Based Split Tunneling
IP address-based Split Tunneling allows routing decisions based on destination IP addresses.
For example, you may want connections to a particular network address to bypass the VPN while other traffic continues through the VPN server.
This can be useful for reaching specific services or network resources that require a direct connection.
However, IP address-based routing requires care.
Some online services use multiple IP addresses, and those addresses may change over time. Adding one IP address does not necessarily control every connection associated with a website or service.
Exclude Mode vs. Include Mode
Some VPN applications provide two approaches to selecting traffic.
Exclude Mode
Most supported traffic uses the VPN, except the applications or IP addresses you explicitly exclude.
Include Mode
Only the applications or IP addresses you explicitly include use the VPN. Other supported traffic uses the regular connection.
Feature | Exclude Mode | Include Mode |
|---|---|---|
Default route | Through the VPN | Outside the VPN |
Selected traffic | Bypasses the VPN | Uses the VPN |
Typical purpose | Make exceptions for certain apps | Protect only selected apps |
Main consideration | Excluded traffic is unprotected by the VPN | Unselected traffic is unprotected by the VPN |
The available modes depend on the VPN application, operating system, and software version.
Why Would You Use Split Tunneling?
Split Tunneling is useful when you need different applications or connections to behave differently.
Here are some common situations where it can help.
1. Accessing Local Services While Using a VPN
Some local services may not work as expected when traffic is routed through a remote VPN server.
These can include certain network-based applications, business tools, or services that expect a connection from your regular network.
Split Tunneling may allow you to keep the VPN active for other activities while routing the required connections directly.
2. Using Applications That Have VPN Compatibility Issues
Some applications may reject VPN connections or behave differently when they detect a VPN server's IP address.
If a particular application needs your regular network connection, Split Tunneling can provide a way to bypass the VPN for that application.
This avoids the need to disconnect the VPN entirely.
3. Managing Work and Personal Applications
You may want some applications to use a VPN while others remain on your standard connection.
For example, you could use a VPN-protected browser for certain activities while allowing an application that depends on local network access to connect directly.
This provides greater control over how different activities use your network.
4. Improving Compatibility with Online Games
Online games can be sensitive to latency, routing, and connection stability.
In some situations, a direct connection may perform better than a VPN connection.
Split Tunneling lets you configure an eligible game to bypass the VPN while keeping other applications connected through it.
However, a direct route does not guarantee lower latency. Actual performance depends on your ISP, game server, network conditions, and routing.
5. Managing Connections to Specific IP Addresses
Some network services require access to a specific IP address or network range.
When IP-based Split Tunneling is supported, you may be able to define routing rules for those destinations.
This can be useful for specialized applications, network resources, or services that require a particular connection route.
Benefits of VPN Split Tunneling
Split Tunneling offers several practical advantages.
More Control Over Your Internet Traffic
The main benefit is flexibility.
Instead of sending all supported traffic through one route, you can decide which connections require VPN protection and which can use the regular network.
Better Compatibility with Certain Applications
Applications that experience problems while connected to a VPN may work more reliably when they use the direct internet connection.
This can reduce the need to turn your VPN on and off throughout the day.
More Flexible Network Access
Split Tunneling can help manage connections to local or specialized network resources without requiring you to disconnect the VPN for everything else.
Potential Performance Improvements
Routing selected traffic outside the VPN can reduce the amount of data passing through the VPN tunnel.
In certain circumstances, this may improve performance for excluded applications.
However, Split Tunneling does not automatically increase internet speed. Its impact depends on your network, application, and VPN connection.
A More Personalized VPN Experience
Different applications have different connectivity requirements.
Split Tunneling allows you to configure your VPN around those requirements instead of relying on one routing rule for every application.
Full Tunnel vs. Split Tunnel VPN: What's the Difference?
A full-tunnel VPN generally routes supported internet traffic through the VPN connection.
A split-tunnel VPN applies selective routing rules.
Feature | Full Tunnel VPN | Split Tunnel VPN |
|---|---|---|
Traffic routing | Supported traffic uses the VPN | Traffic follows selected routing rules |
VPN coverage | Broad coverage | Coverage depends on configuration |
Application flexibility | Limited | More customizable |
Local service compatibility | May require additional configuration | Can improve compatibility |
Traffic outside the VPN | Generally minimized | Intentionally allowed for selected traffic |
Best for | Users who want consistent VPN routing | Users who need selective connections |
Neither approach is automatically the best choice for everyone.
Full tunneling is generally simpler when you want all supported traffic to remain inside the VPN.
Split Tunneling is more useful when specific applications or destinations need different routes.
How to Use Split Tunneling with SyncVPN
SyncVPN includes a Split Tunneling section designed to help you customize which applications and IP addresses are protected by your VPN connection.
The exact configuration controls may vary depending on your operating system and application version.
Step 1: Open SyncVPN
Launch the SyncVPN application on your device.
Make sure you are using an up-to-date version of the application.
Step 2: Open the Split Tunneling Settings
Navigate to the application's settings and find Split Tunneling.
This section is where you can review the available options for managing traffic routing.
Step 3: Enable Split Tunneling
If your version provides an enable/disable switch, turn on Split Tunneling.
Review the available routing options before selecting any applications or IP addresses.
Step 4: Choose Your Applications or IP Addresses
Depending on the available controls, select the applications or destination IP addresses you want to route through or outside the VPN.
Before making changes, decide what you want to achieve.
For example:
Keep a particular application protected by the VPN.
Allow a local application to use the direct connection.
Route traffic for a specific destination IP address according to your network requirements.
Check whether your version uses inclusion rules, exclusion rules, or another configuration method.
Step 5: Save or Apply Your Settings
Save or apply your configuration using the controls available in your application.
Some changes may require the VPN connection or affected applications to restart before the new routing rules take effect.
Step 6: Verify Your Connection
After configuring Split Tunneling, check that the selected applications behave as expected.
For applications that use websites, you may be able to compare the public IP address seen through the VPN route with the address seen through a direct route.
Remember that an IP check in one application does not verify the routing behavior of every application on your device.
Important: The options shown in SyncVPN can differ between operating systems and app versions. Follow the available controls in your installed version rather than assuming every platform provides identical settings.
What Happens After You Enable Split Tunneling?
Once Split Tunneling is configured, your device uses the routing rules defined in the VPN application.
Traffic selected to use the VPN travels through the VPN tunnel.
Traffic configured to bypass the VPN uses the regular network route.
For example, if an application is excluded from the VPN:
Its internet traffic may use your regular public IP address.
It will not receive the VPN tunnel's encryption for that excluded traffic.
Its connection performance may differ from applications using the VPN.
It may interact with websites and services differently from VPN-protected applications.
This behavior is expected.
Split Tunneling intentionally allows different traffic to follow different routes.
Is VPN Split Tunneling Safe?
Split Tunneling can be used safely, but its privacy implications are important.
The VPN protects traffic that actually passes through its encrypted tunnel.
Traffic routed outside the VPN does not receive that VPN tunnel protection.
For example, an excluded application may expose your regular public IP address to websites and online services.
Your internet service provider may also be able to observe connection information associated with traffic that bypasses the VPN, subject to other protections such as HTTPS.
This does not mean Split Tunneling is inherently insecure. It means you are choosing which connections receive VPN protection.
To use it responsibly:
Exclude only applications or destinations that need a direct connection.
Keep privacy-sensitive applications inside the VPN when appropriate.
Review routing settings after application or operating-system updates.
Avoid assuming that Split Tunneling protects every connection automatically.
Test your configuration when privacy is especially important.
The key is understanding which traffic is protected and which is not.
Does Split Tunneling Affect DNS or IP Address Privacy?
It can.
DNS is used to resolve domain names into IP addresses.
The way DNS requests are handled under Split Tunneling depends on the operating system, VPN software, and routing configuration.
Some applications may use system-level DNS services, while others can use their own DNS mechanisms.
Similarly, a rule based on an application's traffic may not always cover every background process associated with that application.
If you need strict control over DNS or IP address exposure, verify the actual behavior of your VPN configuration.
Do not assume that excluding or including an application automatically defines the routing of every related network request.
Split Tunneling vs. Kill Switch: Can They Work Together?
Split Tunneling and Kill Switch perform different functions.
Split Tunneling controls which traffic uses the VPN.
Kill Switch is designed to block affected internet traffic if the VPN unexpectedly disconnects.
Feature | Split Tunneling | Kill Switch |
|---|---|---|
Main purpose | Control traffic routing | Prevent traffic exposure during VPN failure |
Selects VPN-protected connections | Yes | Not its primary purpose |
Intentionally allows direct connections | Depending on configuration | Not inherently |
Responds to VPN disconnections | Not its primary purpose | Yes |
Main benefit | Flexibility | Connection privacy protection |
Whether the two features work together depends on the VPN application and operating system.
Some implementations support both simultaneously, while others restrict certain combinations.
If you use both features, check how the Kill Switch treats traffic intentionally excluded from the VPN.
Do not assume that enabling Kill Switch automatically blocks every direct connection permitted by Split Tunneling.
Why Is Split Tunneling Not Working?
If Split Tunneling is not behaving as expected, several factors may be responsible.
1. Your Changes Have Not Taken Effect
Some routing changes require a VPN reconnection or application restart.
Try disconnecting and reconnecting the VPN, then restart the affected application if necessary.
2. The Wrong Application Was Selected
Check whether you selected the intended application.
Some software uses multiple background processes or separate executables, which can affect application-based routing.
3. The IP Address Has Changed
If you use IP-based Split Tunneling, the destination service may no longer use the address in your configuration.
Review the relevant IP address before assuming the feature has failed.
4. Your Operating System Has Different Limitations
Split Tunneling capabilities may differ across operating systems.
Some platforms support application-based rules, while others may have more restricted options.
Confirm which features are available in your version of SyncVPN.
5. Another Network Setting Is Interfering
Firewalls, security software, proxy settings, and other network configurations can affect how applications connect.
If routing behavior is unexpected, review any additional software that manages your network traffic.
6. The Application Needs to Be Updated
An outdated VPN application may not include recent improvements or compatibility fixes.
Check whether an update is available for SyncVPN.
Best Practices for Using Split Tunneling
A good Split Tunneling configuration starts with a clear purpose.
If you only need one application to bypass the VPN, begin with that application rather than creating a large number of routing exceptions.
Keep your configuration simple enough to understand and maintain.
Whenever you make changes, confirm that the intended applications and destinations are using the expected connection route.
It is also worth reviewing your settings periodically, especially if you install new applications or change networks frequently.
If your priority is protecting all supported traffic through the VPN, a full-tunnel connection may be the more appropriate choice.
Frequently Asked Questions About VPN Split Tunneling
What is VPN Split Tunneling?
VPN Split Tunneling is a feature that allows selected applications or connections to use the VPN while other traffic uses the regular internet connection. It provides more control over how your device routes internet traffic.
Should I Enable Split Tunneling?
Enable Split Tunneling if you have a specific reason to route certain applications or destinations outside or inside the VPN. If you want all supported traffic protected by the VPN, keeping Split Tunneling disabled may be simpler.
Does Split Tunneling Make My Internet Faster?
Not necessarily. Bypassing the VPN for selected applications can sometimes improve their performance, but the result depends on your internet connection, routing, and network conditions.
Does Split Tunneling Hide My IP Address?
Only traffic routed through the VPN generally benefits from the VPN server's public IP address. Applications that bypass the VPN may expose your regular public IP address.
Can I Choose Which Apps Use the VPN?
Application-based Split Tunneling allows you to apply routing rules to selected applications. The available controls depend on your VPN application and operating system.
Can I Use Split Tunneling for Specific IP Addresses?
Some VPN applications, including the Split Tunneling interface shown in SyncVPN, provide options related to IP address routing. Exact capabilities depend on the installed version and platform.
Is Split Tunneling Better Than a Full VPN Connection?
It depends on your needs. Split Tunneling offers more flexibility, while full-tunnel routing is generally simpler for users who want broad VPN coverage without intentional exceptions.
Can Split Tunneling Cause IP Leaks?
Traffic intentionally routed outside the VPN can reveal your regular public IP address. That is an expected result of the configuration rather than necessarily a software leak. Unintended routing may also occur because of misconfiguration or implementation limitations.
Does Split Tunneling Work on Every Device?
No. Feature availability and functionality vary between VPN applications, operating systems, and versions. Check your application's settings to confirm what is supported on your device.
Can I Use Split Tunneling and Kill Switch at the Same Time?
It depends on the VPN application and platform. Some implementations support both features, but their interaction may be limited or require additional configuration.
Final Thoughts
VPN Split Tunneling gives you more control over how your internet traffic is routed.
Instead of choosing between using a VPN for everything or turning it off completely, you can configure different connection paths for different applications or destinations.
This can improve compatibility, support specific network requirements, and make everyday VPN use more flexible.
However, it is important to remember that traffic excluded from the VPN does not receive the VPN tunnel's protection.
For SyncVPN users, Split Tunneling provides a way to manage which applications and IP addresses use the VPN connection.
Start with a simple configuration, review your routing choices carefully, and verify that your applications behave as expected.
The best setup is one that gives you the flexibility you need without unintentionally exposing traffic you intended to protect.